Developer (free)
$0USD / month
Free forever SonarQube Team Plan for private projects up to 50k lines of code, with no credit card required.
- Private projects up to 50k LOC
- No card and no expiry
- Works with major DevOps platforms
AI Code Review & Testing Tools
PRODUCT OVERVIEW
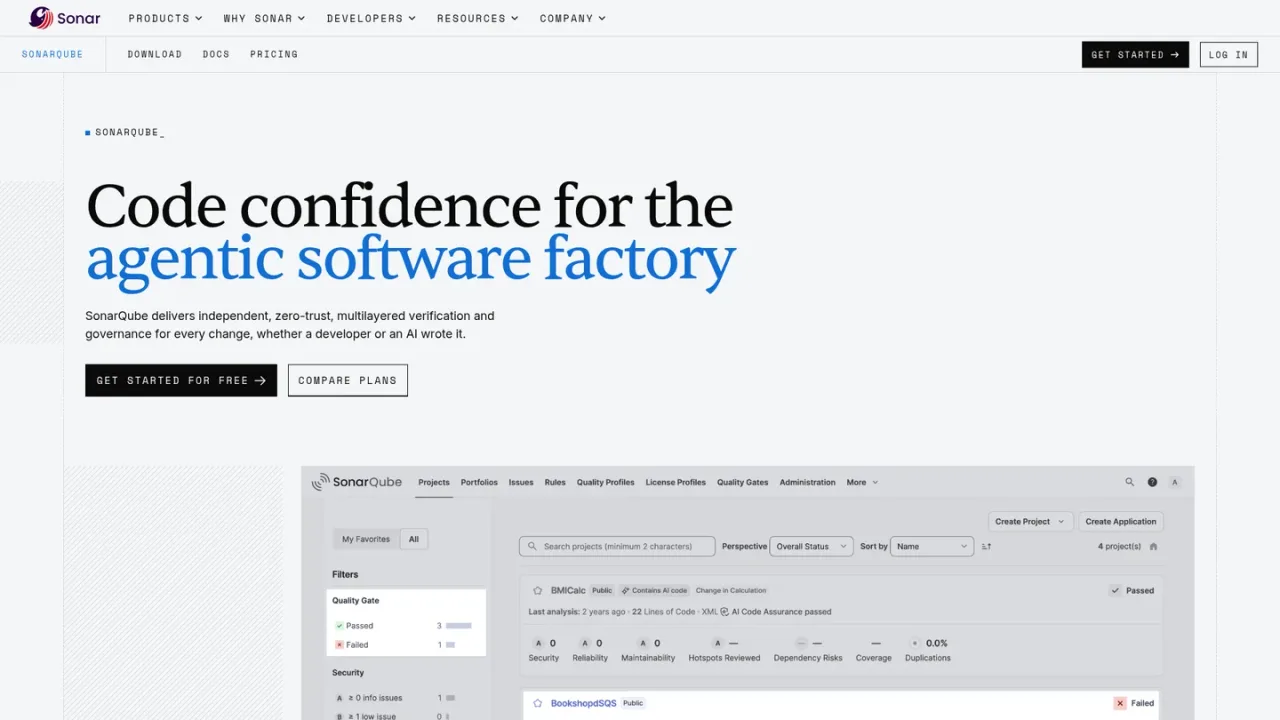
SonarQube is Sonar's code verification and governance platform. It checks every change—whether written by a developer or an AI agent—for bugs, vulnerabilities and maintainability issues, applies your quality gates and records the result. It runs in the IDE, in coding agents, in pull requests and in CI/CD pipelines, on SonarQube Cloud or a self-managed Server. It supports 45+ languages and frameworks, includes SAST and taint analysis, secrets detection and infrastructure-as-code scanning, and adds SCA and Advanced SAST with Advanced Security. Connected mode keeps IDE and pipeline rules aligned, and portfolio dashboards show team progress. AI CodeFix suggests fixes, while the Remediation and Hunter agents open verified pull requests and hunt logic flaws. A free tier and Community Build are available, with paid Team and Enterprise plans.
Sign up for SonarQube Cloud or install SonarQube Server, then connect a repository from GitHub, GitLab, Bitbucket or Azure DevOps to start analysis.
Trigger an analysis on a branch or pull request; SonarQube reports bugs, vulnerabilities and maintainability issues and shows the quality gate result.
Integrate with your build pipeline so a failing quality gate can block the merge, stopping problems at the pull request rather than in production.
Install the free SonarQube for IDE extension and enable connected mode so developers see the same rules the pipeline enforces before committing.
Use the MCP Server, CLI or agent plugins so coding agents receive your standards and check their own output during the session.
Verifying AI-generated code against the same rules and quality gates as developer-written code
Blocking merges when a quality gate fails in pull requests
Finding injection flaws and vulnerabilities with SAST and taint analysis
Catching code secrets during development
Scanning infrastructure as code
Securing open source dependencies with SCA
Producing audit reports against OWASP Top 10, CWE Top 25 and PCI DSS
Keeping IDE and CI/CD standards consistent across teams
SonarQube is the platform that verifies code, whether a developer or an AI agent wrote it, before it ships. It checks every change for bugs, vulnerabilities and maintainability issues, applies quality gates and records the result.
Choose Cloud if you want verification running quickly with Sonar hosting and maintaining it. Choose Server if code and findings must stay inside your perimeter, including air-gapped environments.
Yes. SonarQube includes SAST and taint analysis that find injection flaws and other vulnerabilities across files and functions, plus secrets detection and infrastructure-as-code scanning. Advanced Security adds SCA and Advanced SAST for third-party code.
Yes. SonarQube Community Build and the free tier of SonarQube Cloud let you start at no cost, and SonarQube for IDE is free to install. Paid plans add enterprise capabilities such as advanced security analysis, governance, reporting and support.
SonarQube supports more than 45 languages, frameworks and Infrastructure-as-Code platforms, including Java, JavaScript, TypeScript, Python, C#, C++, PHP and Kotlin.
SonarQube analyzes every branch and pull request and shows the quality gate result in the PR. It works with GitHub, GitLab, Bitbucket and Azure DevOps, and with build tools such as Jenkins, CircleCI and Harness; a failing gate can block the merge.
It checks AI-generated code the same way it checks developer-written code: independently, against the same rules and quality gates. Agents get standards and real-time feedback through the MCP Server, CLI and agent plugins, and every pull request is reviewed before merge.
AI CodeFix uses large language models to suggest a fix for an issue SonarQube finds, for both AI-generated and developer-written code. You review the suggestion in your IDE with SonarQube for IDE connected to SonarQube Cloud or Server.
Prices shown in USD as listed on Sonar's plans and pricing page. A 14-day trial is offered; the free tier never expires. Enterprise pricing is quoted by sales.
Free forever SonarQube Team Plan for private projects up to 50k lines of code, with no credit card required.
Entry paid plan for teams under 50 developers, set up without a sales call, including SonarQube Team and Advanced Security.
AI code review add-on that reviews every pull request in full context, writes fixes and iterates until CI passes.
Plan for organizations over 50 developers, combining SonarQube Enterprise with Advanced Security, Gitar, Sonar Vortex and the Remediation and Hunter agents.
Free forever access for public, OSI-licensed repositories, with the same features as the paid Pro plan.
COMMUNITY REVIEWS
No reviews yet.

Trae offers TraeCode, an AI coding engineer, and TraeWork, a professional AI work assistant, available via download and web.